- Posts: 220
- Thank you received: 0
Check out address pop-up window is empty
- clairewang
-
 Topic Author
- Offline
Less
More
10 years 6 months ago #238629
by clairewang
Check out address pop-up window is empty was created by clairewang
-- HikaShop version -- : 2.5
-- Joomla version -- : 3.3.6
-- PHP version -- : 5.3.29
-- Browser(s) name and version -- : Chrome 51
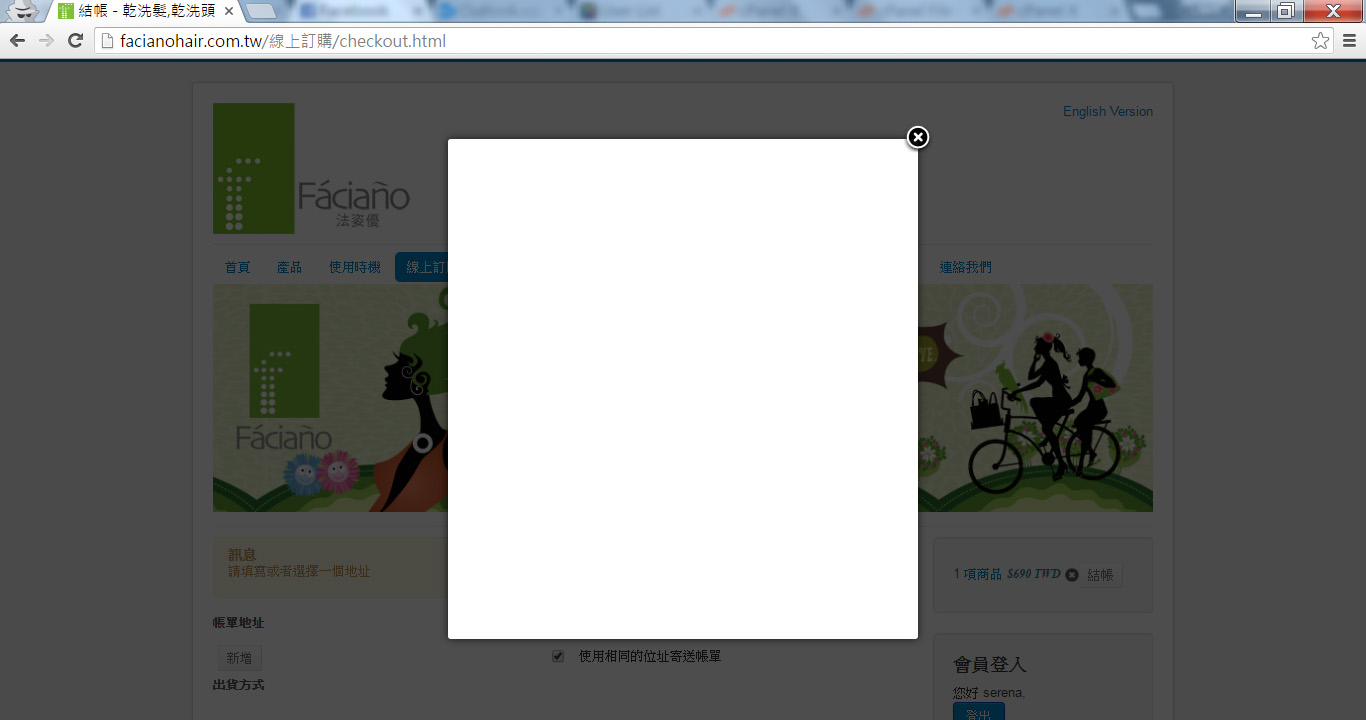
-- Error-message(debug-mod must be tuned on) -- : Check out address pop-up window is empty
Dear all,
Why is the Check out address pop-up window empty?
I did redirect 301 for some websites for www to none www, index.php to none....
But after I found out empty, I deleted those codes but its still empty. Please help as soon as you can, since customers can't buy products. So much appreciation to you!!
-- Joomla version -- : 3.3.6
-- PHP version -- : 5.3.29
-- Browser(s) name and version -- : Chrome 51
-- Error-message(debug-mod must be tuned on) -- : Check out address pop-up window is empty
Dear all,
Why is the Check out address pop-up window empty?
I did redirect 301 for some websites for www to none www, index.php to none....
But after I found out empty, I deleted those codes but its still empty. Please help as soon as you can, since customers can't buy products. So much appreciation to you!!
Please Log in or Create an account to join the conversation.
10 years 6 months ago #238647
by Xavier
Replied by Xavier on topic Check out address pop-up window is empty
Hi,
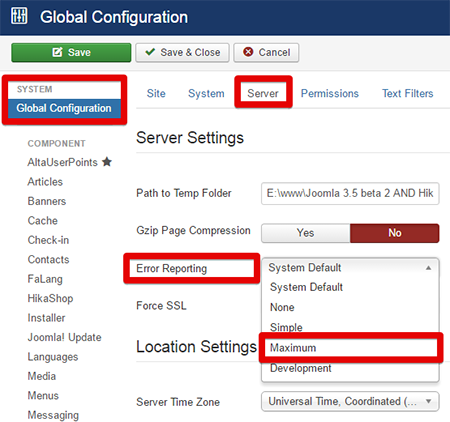
Could you set the Joomla error reporting level to "maximum" and see the displayed error ?
Generally when there is a white page like that, it is due to a PHP fatal error.
Could you set the Joomla error reporting level to "maximum" and see the displayed error ?
Generally when there is a white page like that, it is due to a PHP fatal error.
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 5 months ago #238980
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
Hi Xavier,
Do you mean Debug System turns Yes? I don't see errors.
Do you mean Debug System turns Yes? I don't see errors.
Please Log in or Create an account to join the conversation.
10 years 5 months ago - 10 years 5 months ago #238982
by Philip
Replied by Philip on topic Check out address pop-up window is empty
Hello,
Xavier means the "Error reporting" you can reach here in System => Global Configuration, in Server tab, see screenshot on below :
Awaiting news from you.
Regards.
Xavier means the "Error reporting" you can reach here in System => Global Configuration, in Server tab, see screenshot on below :
Awaiting news from you.
Regards.
Last edit: 10 years 5 months ago by Philip.
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 5 months ago #239084
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
I changed the .htacess file and it looks fine now, so even I turned this on, no error report showing up. But I do have two .htacess files that is one bad one good. Could you see the difference and then we can know why it works for one, not the other?
Please Log in or Create an account to join the conversation.
10 years 5 months ago #239171
by nicolas
Replied by nicolas on topic Check out address pop-up window is empty
Hi,
Well, I don't know what you did, but I did a test on your website and the popup is working just fine:
take.ms/YYIB6
Well, I don't know what you did, but I did a test on your website and the popup is working just fine:
take.ms/YYIB6
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 5 months ago #239185
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
As I told you, I replaced the .htacess file. If you are willing to see these two files, you can teach me how different since I didn't write these two files. Thanks a lot.
Please Log in or Create an account to join the conversation.
10 years 5 months ago #239254
by nicolas
Replied by nicolas on topic Check out address pop-up window is empty
I don't know what you mean by "I replaced the .htacess file".
What .htaccess ? What was in it ? What other .htaccess file did you replace it with ? What is in this new .htaccess file ?
And also, if you found the solution with the .htaccess isn't this case closed ? Or do you still have a problem ?
What .htaccess ? What was in it ? What other .htaccess file did you replace it with ? What is in this new .htaccess file ?
And also, if you found the solution with the .htaccess isn't this case closed ? Or do you still have a problem ?
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 5 months ago #239834
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
I found out a problem, I get every two days someone write these codes in my .htacess files and I have 404 errors all redirect to Japenese websites. Today They code in my .htacess again to only have these codes in the file and also changed my sitemap, index.php. And these codes also causes the address pop-up window blank. The hosting said the plugins has security holes. Do you see any problem at your software from security?
RewriteEngine On
RewriteRule ^(.*)-(.*)-(.*).xacb$ index.php?site=$1&id=$3&temp=$2 [L]
RewriteRule ^(.*)-(.*)-(.*).html$ index.php?site=$1&id=$3&temp=$2 [L]
RewriteEngine On
RewriteRule ^(.*)-(.*)-(.*).xacb$ index.php?site=$1&id=$3&temp=$2 [L]
RewriteRule ^(.*)-(.*)-(.*).html$ index.php?site=$1&id=$3&temp=$2 [L]
Please Log in or Create an account to join the conversation.
10 years 5 months ago #239841
by nicolas
Replied by nicolas on topic Check out address pop-up window is empty
Hi,
There are no known vulnerabilities in HikaShop.
If you already have been hacked, even updating all your extensions and Joomla to the latest version to fix the holes won't be enough. You will still have the infected files. So you need your website to be looked at by a professional. I would recommend to contact www.aesecure.com/en/
They can do that for you for a relatively low price.
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 5 months ago - 10 years 5 months ago #239943
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
Thanks a lot for your info.
I asked him, he charges Euro 200, not low price. Is he trust worthy?
And since we have scan and clean the local computer files also the hosting said there is no virus with the whole files, do you still think it's not any plug-in holes? There is still virus files?
I asked him, he charges Euro 200, not low price. Is he trust worthy?
And since we have scan and clean the local computer files also the hosting said there is no virus with the whole files, do you still think it's not any plug-in holes? There is still virus files?
Last edit: 10 years 5 months ago by clairewang.
Please Log in or Create an account to join the conversation.
10 years 5 months ago #239947
by nicolas
Replied by nicolas on topic Check out address pop-up window is empty
Hi,
Yes, I know him personally. We've met at many JoomlaDays throughout the years.
A virus scan is different from a website hack scan. So not finding any virus doesn't mean that your website is clean. It's best to give that to a professional like him who knows what to look for and has the necessary tools for it. His security solution, AeSecure can keep your website secure in the future.
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 5 months ago #240213
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
Thank you, Nicolas, I am planning upgrading Joomla 3.3.6 to the newest to protect, also with the other plugins/ Will it ruin any hikashop setup or layout?
Please Log in or Create an account to join the conversation.
10 years 5 months ago #240215
by nicolas
Replied by nicolas on topic Check out address pop-up window is empty
Hi,
If you also update hikashop to the latest version (if you don't have it already ) it should not be a problem as it is compatible with the latest version of joomla.
If you also update hikashop to the latest version (if you don't have it already ) it should not be a problem as it is compatible with the latest version of joomla.
Please Log in or Create an account to join the conversation.
- clairewang
-
Topic Author
- Offline
Less
More
- Posts: 220
- Thank you received: 0
10 years 4 months ago - 10 years 4 months ago #241626
by clairewang
Replied by clairewang on topic Check out address pop-up window is empty
Hi dear,
I found lines of Japense words obviously are the previous hacking in the email signup requestion notification. Do you know where to delete those words? Does it mean there is hole for hackers get in for Hikashop? Thank you very much.
您好 沈:
感謝您在 http://.com 註冊。
您必須點擊下面的連結來啟動您的帳號,然後您才可以繼續處理您的訂單。
http://.com/index.php?option=com_hikashop&ctrl=checkout&task=activate&activation=7649a898f7eed1c98c6d0e149b3ce3b5&infos=eyJwYXNzd2QiOiI4NDYwNDI4MCIsInVzZXJuYW1lIjoid2lsbGlhbSJ9&page=checkout&id=296&Itemid=116&lang=
パールネックレス/12mm 指輪 黒蝶 ビジネスシューズ 真珠 モロッカンオイル ペンダント 米
facianohair.com.tw
【送料無料】 K18 WG 真珠 パール コインケース ネックレス タヒチ 黒蝶真珠 綿100% ブラックパール 黒真珠 フォーマル パーティー 結婚式 冠婚葬祭 【_包装】 ムーンレーベル 。パールネックレス/12mm 黒蝶 レースアップ 真珠 ペンダント
您可以使用下面的帳號和密碼登入我們的網站:
名 : william
Last edit: 10 years 4 months ago by clairewang.
Please Log in or Create an account to join the conversation.
10 years 4 months ago #241644
by nicolas
Replied by nicolas on topic Check out address pop-up window is empty
Hi,
No. Once a hacker get in the website, they can modify anything. HikaShop, another extension, Joomla, etc.
So the fact that the registration notification is modified doesn't mean that the hackers used a hole in HikaShop to get access to the website.
It might have been done through a translation override or a modification of the translation file of HikaShop so check both in the HikaShop configuration:
www.hikashop.com/download/languages.html
It could also have been done by editing the email files so check them in the folder media/com_hikashop/mail/
Please Log in or Create an account to join the conversation.
Time to create page: 0.147 seconds